An assurance user is a read-only login for an external auditor or assurer. They can view and download everything in your account, and change nothing. Every write is refused, whatever they try, with one exception: where your plan includes assurance sign-offs (Footprinting and above), they can sign off a product and revoke their own sign-off.
Adding an assurance user
A Global Admin opens Settings > Company > Users and clicks New user.
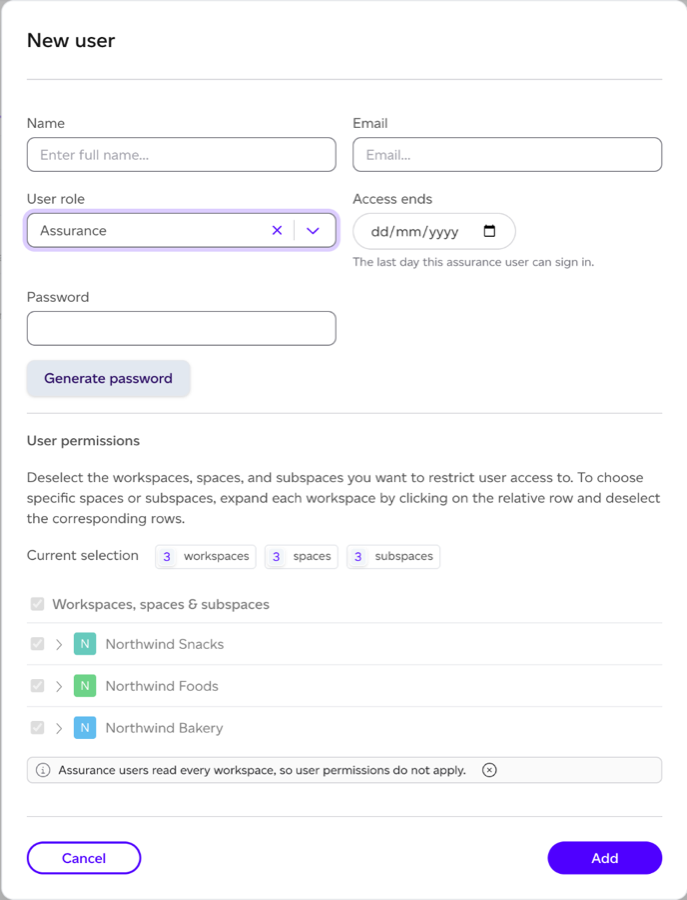
- Enter their Name and Email.
- Choose Assurance as the User role. It cannot be combined with another role.
- Set Access ends: the last day they can sign in, from tomorrow onwards. It is required: an engagement ends, so its access does too.
- If your account signs in with single sign-on, choose how they sign in under Signs in with: A password, for someone outside your organisation (the default) or Your single sign-on, for a colleague. Their read-only access is the same either way.
- Click Add.
Someone who signs in with a password receives an invitation email saying it is read-only assurance access to your account, with its end date and a temporary password to sign in with.
Assurance users see every workspace, so workspace permissions do not apply. The Assurance role is not offered on accounts whose subscription our team manages.
You can have up to two active assurance users by default; contact us if an engagement needs more. To change an end date later, use Edit user role on their row, where a chip shows Access until the date, or Access ended.
What an assurance user sees
A bar across the top of every page says Assurance mode, names your account as the one they are viewing read-only, and gives the date their access ends. Every create, edit, import and other write control is gone from their screens: the product editor, its dialogs, lists and report lists. They can open products and their contents (restricted products included, read-only), reports, Home, the company rollup and the Registry, download what they see, and read the Changes in the activity log. On the Registry they can read everything and change nothing.
Signing off a product
Where your plan includes assurance sign-offs, a product's report shows an assurance user Sign off in its header. A sign-off records the firm, the standard, the level of assurance, an engagement reference, the assurance statement and the date it is valid until. Everyone in your organisation then sees where it stands on the report, the product's summary PDF carries it with a QR code, and anyone can check it on a public verify page. The auditor who signed it can revoke it; a Global Admin can hide it. See How do I sign off a product as an assurance provider?
After the end date, they can no longer sign in, and an open session stops with Your access has ended.
What is recorded
The records and reports an assurance user opens, what they download (a bulk export names the products in it) and their sign-ins are recorded on the Assurance activity tab of the activity log, kept apart from the change log and visible to Global Admins.